Trusted by brands we've built for
500+
Assessments delivered
CREST & CHECK
Qualified consultants
48h
Critical findings alerted
NDA
On every engagement
Design Secure Systems from the Ground Up
Security architecture is the foundation everything else rests on. Flat networks, overly permissive firewall rules, standing administrative access and legacy perimeter-based designs are among the leading causes of successful breaches, and most of them are entirely preventable.
Our security architects review your existing design, identify the structural weaknesses that tactical tooling cannot fix, and produce a prioritised roadmap that strengthens your defences without demanding a rebuild or a bottomless budget. Most engagements move from review to an agreed improvement plan inside four to six weeks.
- Network segmentation and micro-segmentation strategy
- Zero trust architecture design and implementation planning
- Cloud security architecture review across Azure, AWS and Google Cloud
- Identity and access management architecture, including Entra ID and Active Directory
- Firewall, VPN and perimeter security review
- Defence-in-depth layering and control mapping to CIS v8 and ISO 27001
This is particularly valuable after a cloud migration, following an acquisition or merger, when preparing for ISO 27001 or Cyber Essentials Plus, or when a penetration test has surfaced issues that feel structural rather than isolated.
A review establishes what your target architecture should look like, what stands between you and it, and what order to close the gaps in. Because it addresses design rather than individual vulnerabilities, the benefit compounds. Every system built afterwards inherits the segmentation, access model and logging standards the review defined, which is why organisations that invest here tend to see fewer repeated findings in later penetration tests.
Security Architecture
"Expert review and redesign of your security architecture, applying defence-in-depth, zero trust and CIS v8 benchmarks to build a resilient, future-proof posture."
What We Deliver
Architecture Review
analysis of your current infrastructure, design decisions and control effectiveness, reviewing network diagrams, firewall rule sets, cloud configuration and IAM policy against best practice and your own business requirements.
Defence-in-Depth Design
layered architecture where no single control failure leads to full compromise, with control mapping from perimeter to data and pragmatic compensating controls for legacy systems you cannot yet replace.
Zero Trust Implementation
a practical plan to apply never-trust, always-verify principles across identity, device, application and network layers, covering conditional access, device trust, least privilege and continuous validation, sequenced so operations are not disrupted.
IAM Architecture
privileged access management, MFA enforcement, role-based access control, service account hardening, and identity lifecycle governance, plus a review of Active Directory and Entra ID configuration.
Reference Designs & Standards
target-state architecture diagrams, configuration standards and control baselines your IT team or MSP can implement directly, rather than a report that sits unopened.
Change & Assurance Process
a lightweight way for new systems and suppliers to be assessed before go-live, with a checklist and decision record that does not add weeks to projects. Every deliverable is reviewed with your technical lead while it is being written, so the recommendations are already agreed and costed by the time the final document lands.
Architecture Review Process
From current-state assessment to a prioritised improvement roadmap, typically delivered in four to six weeks.
- 01
Weeks 1-2, Discovery & Documentation Review
we gather architecture documentation, diagrams and policies, then analyse topology, firewall and ACL rules, cloud configuration, and privileged and remote access.
- 02
Weeks 3-4, Gap Analysis & Risk Assessment
architectural weaknesses are identified, scored and prioritised, benchmarked against CIS v8 and ISO 27001 controls, with quick wins flagged where risk can be reduced immediately at little cost.
- 03
Weeks 5-6, Roadmap & Recommendations
a technical report, sequenced improvement roadmap, reference architecture designs and an executive presentation suitable for the board, plus an optional walkthrough with your IT provider or MSP.
Engagement Options
Architecture work is scoped to the decision you need to make, whether that is a single review before a certification or ongoing oversight as your estate grows.
Architecture Review
A fixed-scope review of your current design, controls and configuration with a prioritised roadmap. Typical for organisations needing an independent view before a certification, audit or major change.
Target-State Design
A reference architecture built for your business, delivered as diagrams, control baselines and configuration standards your team or MSP can implement directly.
Cloud Landing Zone Review
Assessment of Azure, AWS or Google Cloud foundations, covering identity, segmentation, logging, key management and the guardrails for future workloads.
M&A and Integration Support
Rapid assessment of an acquired estate, a containment plan for urgent issues and an integration roadmap that avoids importing inherited risk.
Ongoing Architecture Oversight
Quarterly design reviews and change assurance, so new systems, suppliers and cloud services are assessed before go-live rather than afterwards.
Virtual CISO
Strategic security leadership alongside the technical work, covering policy, board reporting, supplier assurance, budgets and roadmap ownership.
Each option is scoped against the decision you need to make rather than a fixed bundle, so a single environment review before certification does not become a full programme. Where several workstreams run together, one consultant owns the relationship and keeps the roadmap honest, reporting progress in the same terms your board or insurer uses.
Frequently Asked Questions
If your question is not covered here, a consultant will answer it directly, with no sales script.
Do we need to replace our existing security tools? Rarely. Most architecture gaps are configuration, segmentation and identity problems rather than product gaps. We recommend changes to design and configuration first, and only then discuss tooling, so you are not sold licences you do not need.
How disruptive is a redesign? The roadmap is sequenced so controls can be implemented without business interruption. Quick wins land early and structural changes are planned around your change windows and operational calendar.
Can you work with our cloud provider or MSP? Yes. We regularly deliver alongside managed service providers, supplying the architecture and prioritised guidance while they implement and operate the controls, with clear ownership boundaries agreed up front.
How does this support ISO 27001? The review maps your current and target architecture against ISO 27001 Annex A controls and CIS v8 benchmarks, giving you documented design decisions and evidence for the certification audit.
What does a review cost? Scope and cost are agreed in writing before work starts. A focused review of a single environment is typically delivered in four to six weeks, with fixed-price options available for well-defined scopes.
Benefits & Compliance Alignment
Structurally Secure
architectural improvement closes the fundamental gaps that no amount of tactical tooling can compensate for, and reduces the blast radius of anything that does get through.
Clear Investment Focus
a risk-ranked roadmap means security spend targets the changes with the highest risk reduction, not the loudest vendor pitch, and quick wins are delivered while longer projects are planned.
Built for Growth
architecture designed for your current and near-future state, so new systems, sites and acquisitions slot in without a redesign or a fresh round of exceptions.
Assurance You Can Share
an independent, evidence-based view aligned to ISO 27001, Cyber Essentials Plus and CIS v8, that demonstrates security has been designed rather than inherited.
Works With Your Team
we deliver alongside in-house IT and managed service providers, offering independent assurance and clear prioritised guidance rather than duplicating work already being done.
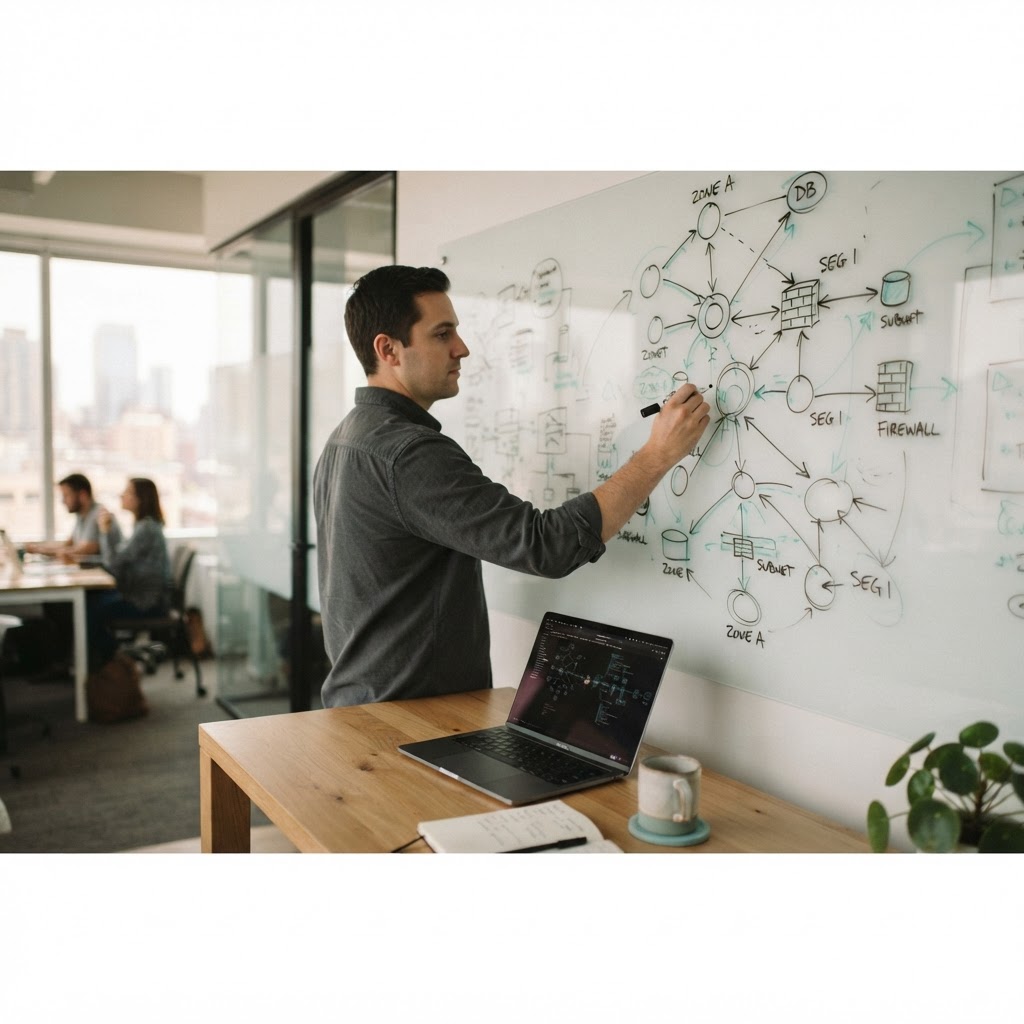
Security Architecture in practice
Get a full SEO report in seconds
Enter your website URL below and we'll run an in-depth analysis covering technical health, keyword performance, competitors, backlinks and content gaps, then follow up with a tailored plan to improve your rankings.
Our experience
Your vision, powered by our expertise. We combine strategic planning with high-level digital experience to ensure your business doesn't just exist online, it thrives.

How we work
A proven process for digital success

01.
Strong Project & Process Management
Our project managers serve as the central hub for all your project requirements. They oversee the complete project life-cycle, from planning and organizing to controlling and deploying key milestones and deliverables aligned with your objectives. Additionally, all projects are overseen by our CTO, who ensures audits and enforcement of quality standards.
02.
Transparent Lines of Communication
We maintain open, transparent communication throughout every phase of your project. You'll always know where things stand, what's happening next, and how your project is progressing against timelines and budget.
03.
In-Depth Analysis of Your Requirements
We take the time to thoroughly understand your business, your audience, and your digital needs before any work begins. This ensures every solution we deliver is precisely aligned with your goals and objectives.
Client reviews
What our clients say
We use Acorn Web Studio for all our website maintenance and SEO marketing for our car body shop repair business. Since they have taken over the SEO we have seen an increase in business locally, which is what we were after. We will soon have them redesign our website.
Gavin Jessop
Verified Google Review
We are a UAE Dubai based business. We needed a new website built to showcase our products and provide information through our website to our clients. At the same time we required digital marketing to be carried out, in particular SEO and LinkedIn Marketing. We partnered with Acorn Web Studio in the UK because the agencies in the UAE let us down time after time. Since we started our working relation we have not looked back. They not only built our website but uploaded 100 products and improved our SEO Google position and LinkedIn profile.
So Pure Water
Verified Google Review
Acorn Web Studio built our new website after we had several issues with our old one and had no support from our previous designer based overseas. They built us a new website and now support us with ongoing maintenance and SEO. Highly recommended.
Naveed
Verified Google Review
Book your free consultation today
Follow these 3 easy steps to start your partnership with us!
Book Your Consultation
Book your consultation at a time and date that suits you and talk to one of our experts.
Obtain Your Free Proposal
After the consultation, we will provide you with a free in-depth proposal on what we can provide you and your business with and the benefits you can expect to see.
Proceed With Your Project
Once you are happy with what we can provide, we can then commence with your project and build a solid working relationship.
Our Stack
Technologies We Master
The tools and frameworks we use to build fast, scalable, and beautiful digital experiences.

WordPress

WooCommerce

Elementor

cPanel

Stripe

PayPal

React

Google Analytics

Google Ads

Cloudflare

MySQL

PHP

JavaScript

Tailwind CSS


Calendly

Shopify

Magento

PrestaShop

OpenCart

Joomla

Drupal

HubSpot

Mailchimp

Meta Ads


Next.js

Node.js

TypeScript

HTML5

CSS3

Figma

Google Tag Manager

Google Search Console

Yoast SEO

Vercel

Sass

Bootstrap

jQuery

Flutter

Swift

Kotlin

Android

Android Studio

Expo

Firebase

Dart

GraphQL

MongoDB

Redis

Docker

GitHub

Apple